
AI Summarize


Share


The Global Privacy Protocol (GPP) is a technical protocol from the IAB Tech Lab, the standards arm of the Interactive Advertising Bureau (IAB), a global advertising trade association. The GPP lets websites and apps capture the privacy and consent choices of a user and transmit them across the digital advertising supply chain. The IAB Tech Lab defines the GPP as "a protocol designed to streamline the transmission of privacy, consent, and consumer choice signals from sites and apps to ad tech providers." It does this by transmitting a GPP string, a compact block of encoded text, that follows an ad request and tells every vendor downstream what choices the user made. In February 2025, the IAB Tech Lab renamed the standard from Global Privacy Platform to Global Privacy Protocol to clarify its status as an open protocol rather than platform software from the IAB, while retaining the GPP acronym.
The GPP serves advertisers, ad tech vendors, and website owners who serve ads across more than one jurisdiction. It simplifies compliance, as businesses face a complex and ever-changing patchwork of data privacy laws, each with its own notice and opt-out duties. It currently defines 27 section IDs, covering the IAB Europe Transparency and Consent Framework (TCF), the IAB Canada TCF, the US National string of the Multi-State Privacy Agreement (MSPA), and 20 US state sections from ID 8 (California) to ID 27 (Rhode Island). This results in a single integration between your Consent Management Platform (CMP) and ad stack, rather than having to build one out for every new state law, making GPP an affordable solution.
This guide will walk you through everything you need to know about the GPP. It explains what the GPP is, how a CMP builds a GPP string, which laws the GPP helps businesses comply with, and how universal opt-out mechanisms (UOOMs) fit in. It explores how the GPP differs from the Global Privacy Control (GPC), a CMP, Do Not Track (DNT), the IAB TCF, and MSPA. The article will review how users implement the GPP, the split between web and mobile, a compliance checklist, and an FAQ section. However, the GPP is only helpful when a Privacy Policy contains tailored and compliant disclosures. Your Privacy Policy underpins every consent signal you send, and the simplest way to build one that matches your business needs is to use the TermsFeed Privacy Policy Generator.
- 1. What Is the IAB Global Privacy Protocol (GPP)?
- 1.1. Who Created the GPP?
- 2. How the GPP Works (The GPP String)
- 2.1. GPP Header
- 2.2. GPP Sections
- 2.3. How GPP Benefits Your Business
- 3. Which Privacy Strings Does the GPP Support?
- 4. Are Businesses Legally Required to Use the GPP?
- 5. What Laws Can the GPP Help You Comply With?
- 5.1. EU GDPR and the IAB TCF
- 5.2. US State Privacy Laws and the GPP
- 5.3. Other Global Privacy Laws (PIPEDA, LGPD, and More)
- 6. Is the GPP a Universal Opt-Out Mechanism (UOOM)?
- 6.1. US State UOOM Deadlines
- 7. GPP vs. Global Privacy Control (GPC)
- 8. GPP vs. Consent Management Platforms (CMPs)
- 9. GPP vs. Do-Not-Track (DNT) Requests
- 10. GPP vs. the IAB Transparency and Consent Framework (TCF)
- 11. The Multi-State Privacy Agreement (MSPA) and the US National String
- 11.1. Who Can Use the US National String?
- 12. GPP on the Web vs. in Mobile Apps
- 13. How to Implement the GPP on Your Website
- 14. How Users Enable the GPP (via the GPC)
- 15. When to Use the GPP (and When You Don't Need It)
- 16. The GPP Timeline (2021-Today)
- 17. GPP String Anatomy: Sections, Headers, and Section IDs (Technical Deep-Dive)
- 18. GPP Implementation Checklist (Step-by-Step)
- 19. GPP and Google Consent Mode / Ad-Platform Requirements
- 20. GPP Glossary: Key Terms Cheatsheet
- 21. GPP and Ad Performance: Does Honoring Opt-Outs Hurt Campaigns?
- 22. IAB GPP: Frequently Asked Questions
- 23. Do You Need a GPP-Ready Privacy Policy?
- 24. Summary and Key Takeaways
What Is the IAB Global Privacy Protocol (GPP)?
The IAB Global Privacy Protocol (GPP) is a technical protocol that lets a website or an app capture the privacy and consent choices of a user and communicate those choices to ad tech providers across the advertising supply chain. The IAB Tech Lab built the GPP on the foundation of the IAB Europe TCF, and it now includes the TCF as one section among many. By including current frameworks and leaving room for new regimes coming online, it makes multi-jurisdiction compliance simpler and more cost-effective.
One of the biggest benefits for businesses is a more seamless experience for users. A CMP reads the opt-out signal already set in the browser of the user, encodes that choice in a GPP string, and attaches that string to the ad request as the page loads. This allows the visitor to opt out of targeted advertising or the sale of personal data without interacting with a cookie consent banner. Downstream, every vendor receives the same instruction at the same moment.
That single-envelope design makes the IAB GPP the only industry signalling mechanism built to carry existing and upcoming US state privacy laws in one place. A CMP identifies the state a visitor is in, applies the rules of that state, and writes the result into the section reserved for it. The same string carries a California choice, a Colorado choice, and a European choice side by side, so one integration answers every jurisdiction you sell into.
Helpfully for businesses that do not have a dedicated data privacy team, the GPP protocol keeps expanding as new laws come into being. For example, in 2025, the IAB Tech Lab added 4 new US state sections: Maryland, Indiana, Kentucky, and Rhode Island, as shown in the screenshot below.

The IAB Tech Lab has committed to releasing six-monthly updates starting in 2026. The goal is to provide greater predictability for businesses as new laws come into effect, eliminating the scramble for compliance each time a bill passes.
There are 3 clear gains for businesses from using the GPP. Firstly, you build one signalling path rather than a new one per state. Secondly, your CMP vendor provides new state coverage rather than your own team. Thirdly, you provide your ad tech partners with a machine-readable record of what each visitor chose. Businesses find that skipping the GPP exposes them to regulatory risk on multiple fronts. Partners who receive no signal keep processing data for visitors who opted out. This potentially creates compliance risk for publishers and other parties in the advertising supply chain if website owners do not communicate opt-out preferences and advertisers do not honor them correctly.
Who Created the GPP?
The IAB Tech Lab created the GPP and released it in 2022. The IAB is a trade body for the digital advertising industry, and focuses on research, education, and policy work. However, its technical arm, the IAB Tech Lab, is its standards arm. This function develops the technical specifications the industry has come to rely on.
The GPP came out of Project Rearc, an initiative the IAB Tech Lab launched in February 2020 to rearchitect digital marketing around consumer privacy after the decline of third-party cookies. The IAB Tech Lab unveiled the GPP on June 1, 2022, following "two years of collaboration with the industry, and consultation processes with technical and legal experts across the globe," as shown below.

The technical and legal aspects of the GPP run separately, allowing it to handle many different regimes at once. For example:
- The IAB Legal Affairs Council supplies the legal interpretation behind the US strings.
- IAB Europe owns the TCF string and the reasoning behind it.
- Local IABs and market participants shape the sections for other jurisdictions as those markets adopt the GPP.
The IAB Tech Lab Global Privacy Working Group then turns that legal analysis into fields, values, and encoding rules.
As the GPP is an open specification published on GitHub under a Creative Commons license rather than a product that requires a subscription or licence fee, you use it to protect your business without cost. However, business owners must still ensure the CMP they pay for implements the published specification rather than a proprietary variant of it, as signals only interoperate when every party encodes them the same way.
How the GPP Works (The GPP String)
At the heart of the GPP is a single, machine-readable GPP string that carries the privacy choices of a user across every jurisdiction that applies to them. The GPP combines the encoding rules of several separate privacy frameworks into one format. A CMP then merges the user preferences into that one string. The string then travels with the ad request, meaning a website, an advertiser, and every ad tech vendor in the chain read the same record of what the visitor agreed to.
The string has two parts. The GPP header works like a table of contents, and the GPP sections hold the actual choices.
GPP Header
The GPP header sits at the front of the string and announces what follows. It carries 3 pieces of information:
- A type value that identifies the string as a GPP string
- A version number for the GPP specification
- A list of the section IDs present in the string
Those IDs appear in the same order as the sections themselves. In practice, a vendor reads the header first, learns that a California section and a European section sit inside, and jumps straight to the one that concerns it. The header avoids every vendor having to parse the whole string to find out whether it contains anything relevant.
GPP Sections
The GPP sections each correspond to one framework or one law. A European section carries the disclosures made to the user, the consent choices of that user, a timestamp recording when the consent happened, and the legal restrictions that apply to individual vendors. A US state section carries a different shape entirely, with fields for notice given, opt-outs exercised for sale, sharing, and targeted advertising and a separate subsection recording whether the browser sent a Global Privacy Control signal. The specification currently defines 27 section IDs, running from ID 1 to ID 27, with Rhode Island the most recent addition.
In the GPP, existing signals turn into sections rather than disappearing. For example:
- The old US Privacy string that answered the California Consumer Privacy Act (CCPA) became section 6.
- The EU TC String that answers the General Data Protection Regulation (GDPR) became section 2.
- The Canadian TCF string became section 5.
Nothing about those frameworks changed in substance, and the vendors who parsed them parse the same content in the same format. The only difference is that it wraps them in an envelope that carries the rest of the world alongside them.
The structure of the GPP string lets policy bodies keep control over what each jurisdiction demands. So IAB Europe determines what the TCF section encodes and the IAB Legal Affairs Council determines what the US sections encode. The IAB Tech Lab just supplies the standard way to encode any of it. That separation is why a new state law becomes a new section rather than a new specification, and why the GPP survives legal changes that would break purpose-built signals.
How GPP Benefits Your Business
Your practical takeaway is short. Confirm that the GPP string reaching your ad requests carries a section for every state your visitors come from, and decode a live string from your own site rather than trusting the CMP dashboard, because the dashboard reports what the CMP intended to send rather than what your ad server received.
To ensure your business is utilizing the GPP string correctly, check whether your CMP sends a signal for every state your customers live in. Then test a real page on your own site to confirm the signal arrives. The settings screen of a CMP shows what you turned on, and a test shows what your advertising partners receive, which are not always the same thing.
Which Privacy Strings Does the GPP Support?
GPP doesn't replace every signal; it groups them so each existing privacy string becomes a section inside one GPP string rather than a separate transmission. The GPP-supported strings currently cover 4 families, shown in the table below.
| GPP Privacy String | Coverage |
| IAB Europe Transparency and Consent Framework (TCF) string | The European Economic Area (EEA) and the UK |
| IAB Canada TCF string | Canada |
| MSPA US National string | The United States as a single signal, for MSPA signatories and certified partners |
| US state strings | 20 states — California, Colorado, Connecticut, Delaware, Florida, Indiana, Iowa, Kentucky, Maryland, Minnesota, Montana, Nebraska, New Hampshire, New Jersey, Oregon, Rhode Island, Tennessee, Texas, Utah, and Virginia |
The US National string answers every US state law through one set of fields which removes the need to emit a separate section per state. Only MSPA signatories and MSPA-certified partners send it, and everyone else sends the individual state strings instead.
The IAB Tech Lab constantly expands the scope of the GPP as jurisdictions pass new laws, as shown by the addition of new US state laws as their jurisdictions enact them.
Are Businesses Legally Required to Use the GPP?
No, businesses are not legally required to use the GPP. No current privacy law specifically names the GPP or any other protocol or specific technology. However, many US state laws require businesses to honor opt-out signals from visitors, and the GPP is the standard mechanism for conveying that signal to everyone downstream in the jurisdictions it covers.
There are 3 factors that make the GPP close to unavoidable for most businesses:
- 12 states require that businesses honor universal opt-out mechanisms (UOOMs), and the GPP is the standard industry mechanism for transmitting these to advertising partners.
- The IAB Tech Lab deprecated the previous US Privacy String in 2024, leaving no maintained IAB alternative for multi-state signalling.
- Major ad platforms read the GPP string, and Google Ad Manager, AdSense, and AdMob consume it, among others.
The bottom line is that while no law requires using the GPP, in practice it's the most widely accepted way to honor your obligations under state laws. Skip it, and you take on the burden of honoring those opt-outs by other means, and of proving you did.
What Laws Can the GPP Help You Comply With?
GPP helps website owners comply with laws that require capturing and honoring the consent and opt-out choices of users across every jurisdiction that they come from. Its structure accommodates the requirements of a number of different laws at once.
For example, the GDPR wants informed consent recorded before processing begins, while Colorado wants an opt-out of targeted advertising honored, whereas Utah wants notice and an opportunity to opt out of sensitive data processing. Each demand carries its own fields, timing, and legal basis. The GPP consolidates this fragmented picture into one transmission.
EU GDPR and the IAB TCF
The GDPR requires users to give consent freely and that it is specific, informed, and unambiguous before you process personal data for advertising. The GPP carries that consent through the IAB Europe TCF v2.3, and the European section of a GPP string holds the TC String that the TCF defines. The TC String is the encoded record of what a visitor agreed to under the TCF, and it predates the GPP as a standalone signal. The European section records which purposes the user agreed to, which vendors received disclosure, the legal basis claimed for each purpose, and the moment the consent happened.
The GPP helps transmit consent choices collected under the TCF to downstream participants in a standardized format. This assists your compliance with the GDPR throughout the EU/EEA.
US State Privacy Laws and the GPP
While US state laws share similarities around opt-out signals, each has its own specific requirements. To ensure compliance, the GPP carries each one to your advertising partners in the section reserved for that state. The table below breaks down how 4 states differ in terms of the GPP state privacy signals:
| State | Signals the GPP carries |
| California (CCPA/CPRA) | Notice of sale and sharing, opt-out of sale, opt-out of sharing, limits on the use of sensitive personal information |
| Colorado (CPA) | Notice of sharing with third parties, opt-out of sale, opt-out of targeted advertising, opt-in consent for sensitive data |
| Connecticut (CTDPA) | Notice of sharing with third parties, opt-out of sale, opt-out of targeted advertising, opt-in consent for sensitive data |
| Virginia (VCDPA) | Notice of sharing with third parties, opt-out of sale, opt-out of targeted advertising, opt-in consent for sensitive data |
| Utah (UCPA) | Notice of sharing with third parties, opt-out of sale, opt-out of targeted advertising, notice and opportunity to opt out of sensitive data processing |
It's worth noting that California separates "sharing" for cross-context behavioral advertising from "sale." Resultingly, the California section carries both as independent fields, and a visitor opts out of one without opting out of the other. Utah sets a lower bar than its neighbors on sensitive data, asking for notice and an opt-out where Colorado, Connecticut, and Virginia ask for opt-in consent. The remaining state sections follow the Colorado pattern with local variations.
Other Global Privacy Laws (PIPEDA, LGPD, and More)
The GPP includes other non-US and EU jurisdictions. Canada has a dedicated section through the IAB Canada TCF, which supports consent under the Personal Information Protection and Electronic Documents Act (PIPEDA) and the stricter provincial rules in Quebec. The United Kingdom runs on the European TCF section because the UK GDPR retains the consent standard of the EU original.
Currently, Brazil, under the Lei Geral de Proteção de Dados (LGPD), and the Asia-Pacific (APAC) regulations have no dedicated GPP section yet. A business operating there records consent through its CMP and relies on contracts rather than an encoded signal. The IAB Tech Lab adds jurisdictions as local IABs and market participants bring them forward. This protects businesses, as the GPP is a framework built for future expansion, but website owners must check that their CMP is using the latest iteration.
Is the GPP a Universal Opt-Out Mechanism (UOOM)?
Technically, no. The GPP is not itself a UOOM. A UOOM is a browser setting, extension, or device flag the user turns on once, which then announces an opt-out from the sale of personal data, the sharing of personal data, and targeted advertising to every site that person visits. The distinction is that the user owns the UOOM, while the GPP owns the transmission that follows.
In practice, UOOMs and the GPP work as a pair. A CMP detects the UOOM a visitor sends, records it as an opt-out in the relevant state section, and the GPP string carries that decision to every vendor downstream. The GPP supports the recognized UOOMs, the Global Privacy Control (GPC) above all, and each US state section includes a dedicated subsection that records whether GPC was present. GPP UOOM support therefore depends on your CMP detecting the signal in the first place. That design puts the preferences of a user for every applicable jurisdiction in one place.
US State UOOM Deadlines
12 states now require businesses to honor universal opt-out mechanisms. The table below shows the deadlines for enforcement by state.
| State | What the law requires | In force from |
| California | Honor opt-out preference signals for sale and sharing | Sale from August 14, 2020, with sharing added March 29, 2023 |
| Colorado | Honor UOOMs meeting the technical requirements of the Attorney General | July 1, 2024 |
| Connecticut | Honor UOOMs | January 1, 2025 |
| Texas | Honor consumer UOOMs | January 1, 2025 |
| Montana | Recognize global device opt-out settings | January 1, 2025 |
| Delaware | Respond to browser, extension, and device settings | January 1, 2026 |
| Oregon | Recognize browser extension and global device privacy settings | January 1, 2026 |
| Maryland, Minnesota, Nebraska, New Hampshire, New Jersey | Honor UOOMs | Phased across 2025 and 2026 |
The dates cited above have all passed, so businesses must be compliant right now. Regulators focus on whether a signal sent today reaches the partners processing your data. When used correctly, the GPP is the mechanism that evidences the signal reached your partners in compliance with state laws.
GPP vs. Global Privacy Control (GPC)
GPP and GPC both carry privacy preferences, but they do different jobs. The table below breaks down what each does and who maintains it.
| GPP | Global Privacy Control (GPC) | |
| Definition | A protocol for the digital advertising industry | A browser-level universal opt-out mechanism |
| Function | Conveys consent and opt-out signals downstream through the ad supply chain | Flags "do not sell or share my data" on every site a user visits |
| Source | IAB Tech Lab | A coalition of privacy groups, publishers, and browser developers |
| Who controls it | The website or app | The user |
Generally, it is not a case of GPP vs. GPC. They work together, with the GPP reading the GPC flag and recording it in the relevant state section before passing it downstream.
The GPP helps businesses fulfill their legal obligations under data privacy legislation such as the California Consumer Privacy Act (CCPA)/California Privacy Rights Act (CPRA), which require businesses to honor a GPC signal as a valid opt-out request. By recognizing the GPC and carrying it to advertising partners, the GPP helps businesses remain compliant.
GPP vs. Consent Management Platforms (CMPs)
The GPP and a CMP are different tools that work together, with one recording the consent decision and the other transmitting it. A Consent Management Platform (CMP) is the software on your site that handles:
- Obtaining consent from visitors
- Tracking choices
- Storing consent records
The GPP then carries these choices forward to the ad tech vendors who act on them. Both are vital, and neither replaces the other.
The GPP vs CMP division is clear when a visitor arrives. A Consent Management Platform with GPP support identifies the location of the visitor, works out which legal framework applies, and serves the relevant consent notice. Once the CMP has gathered the consent choices, the GPP sends the relevant string downstream to ad vendors.
However, a CMP does more than produce strings. Its functions include:
- A website scanner that finds the cookies and trackers you run.
- An auto-generated Cookie Policy that lists what the scan found.
- A customizable consent banner that collects the choices of visitors.
- A preference center where a visitor returns to change those choices.
- A data subject access request (DSAR) form that handles requests to see, correct, or delete personal data.
A GPP-aware CMP will read and honor the signal without asking the user to input their choices again when the user has already set the GPC ahead of time in a browser. Sometimes, it is not even necessary to display a consent banner. The combination of a GPP-aware CMP and GPC is an experience that satisfies the law and is frictionless for users.
GPP vs. Do-Not-Track (DNT) Requests
DNT was the earlier attempt at a "don't track me" signal. It failed because no law ever required a website to honor it, and major players such as Google ignore it. Do Not Track (DNT) is a browser setting or plugin that tells every site a user visits that the person does not allow tracking for advertising and analytics. It gained a legal footing in January 2014, when amendment AB370 to the California Online Privacy Protection Act (CalOPPA) took effect.
However, while AB370 created a disclosure duty, it went no further. An operator must disclose in its Privacy Policy how it responds to DNT signals, but there is no obligation to respond in any particular way. This resulted in major platforms such as Google deciding not to respond to DNT requests. Over time, browsers dropped the setting, with Firefox becoming the latest to remove it in 2025.
The GPP vs DNT comparison is a difference between a request and an instruction. The problem with the DNT is that it lacked teeth. It was a polite request, rather than an enforceable signal. The CCPA and CPRA changed that by requiring businesses to honor opt-out preference signals, even allowing them to serve as an alternative to displaying a "Do Not Sell or Share My Personal Information" link. The GPP effectively became the successor to DNT. It carries choices that state laws oblige partners to act on across every jurisdiction at once.
GPP vs. the IAB Transparency and Consent Framework (TCF)
The GPP and the TCF are related but serve different scopes, with the Transparency and Consent Framework (TCF) answering one region in depth and the GPP serving many regions at once. The GPP vs TCF distinction comes down to 2 things: scope and focus.
| TCF | GPP | |
| Scope | Exists for European law, built around the GDPR and the ePrivacy Directive, and applies only within the borders of the EU and EEA. A business selling only in Germany runs on the TCF alone. | Reaches across jurisdictions by combining the consent signals of each one into a single transmission. A business selling in Germany and Texas needs the GPP to carry both. |
| Focus | Asks a visitor to make detailed decisions, covering which vendors receive data, which categories of data they receive, which processing purposes apply, and which legal basis supports each one. | Standardizes disparate signals so every party in the supply chain reads them identically. The US sections work at a coarser grain, recording opt-outs from sale, sharing, and targeted advertising rather than permissions for individual vendors. |
In terms of GPP vs TCF, neither approach beats the other. Each matches the law behind it, since the GDPR demands specific consent and US state laws demand a workable opt-out. For this reason, the TCF exists as a section inside the GPP rather than a rival to it. As shown below, the IAB Tech Lab positions the GPP as the route for future signaling and advises adopting it, "as it will be the primary framework where future global consent and preference signaling will be made available."

Given the fact that the GPP is becoming more widely adopted and embeds the TCF, it makes sense for businesses to transition now to simplify compliance.
The Multi-State Privacy Agreement (MSPA) and the US National String
To make a single string work across the US, the IAB created the MSPA, a standard contract that ad industry participants sign so they interpret state privacy laws the same way. The Multi-State Privacy Agreement is a legal instrument rather than a technology. The GPP conveys the signal, while the MSPA settles what the signal means.
The MSPA grew out of the Limited Service Provider Agreement (LSPA), which the IAB released in 2020 for CCPA compliance. The LSPA covered one state and one law. New state laws then arrived quickly and it was hard for the IAB to keep up. Therefore, the IAB rebuilt the framework as the MSPA and aligned it with the GPP, transferring existing LSPA participants across automatically unless participants withdrew.
The US National String exists to serve the National Approach, a term defined in the MSPA. Signing parties agree to apply one consistent standard that meets the strictest requirement among the state laws, rather than negotiating state by state. That agreement allows a single section to speak for the whole country, and is why only MSPA signatories and certified partners send the US National String.
A string listing every state provision without the MSPA behind it carries little practical value. Senders and recipients reconcile the differences between state laws in their own ways, so a publisher treats an opt-out as covering one thing and a vendor treats it as covering another. The signal stops meaning anything reliable at that point. The contract removes the ambiguity before the string ever travels.
The MSPA moves as the law moves. The IAB published the Fifth Amended and Restated Multi-State Privacy Agreement in March 2026, in the most substantial revision since 2023. As shown in the screenshot below, its stated aims are to aid advertiser compliance, simplify privacy law compliance, and reduce friction.

The MSPA treats downstream ad tech partners as service providers by default, with an exception under the CCPA. It lets partners suppress opted-out consumers instead of requiring advertisers to build technical signals of their own.
Who Can Use the US National String?
Only MSPA signatories and MSPA-certified partners can use the US National String, and only those who have agreed to the National Approach. Everyone else sends the individual state strings. This is a critical compliance rule from the IAB itself, as evidenced in the screenshot below.

The string asserts, in machine-readable form, that the sender follows that approach. According to Michael Hahn and Rowena Lam of the IAB, publishers and advertisers that send it without signing "run the risk of making material misrepresentations" about their status in relation to the MSPA. The Federal Trade Commission (FTC) and State Attorneys General enforce against misleading claims of this kind, so the risk sits in the claim rather than the technology.
It is essential that each business checks the published MSPA signatory list before configuring its CMP, because a default setting carries the same legal weight as a deliberate claim. MSPA signatories or MSPA-certified partners send either the US National String or a state-specific string, while non-signatories send and receive only state-specific strings.
GPP on the Web vs. in Mobile Apps
The GPP works across both web and mobile, and the choice a person makes looks identical in each place. However, your website and your app handle that signal differently behind the scenes.
On a website, the GPP API does the work. An API is a standard way for one piece of software to ask another for information, and the GPP API lets the advertising code on your page ask your CMP what the visitor chose. Version 1.1 is the current release, and most CMPs include it.
GPP mobile support works differently, since an app has no web page for that code to sit on. The GPP solves this by fixing where an app stores the choice and what each piece of stored information is called. Advertising code inside your app then looks in the same place every time, whichever CMP put the information there.
The benefit is consistency, as your advertising partners receive the same signal in the same shape from your website and your app. However, it's important to note that a website and an app keep their records separately. So a user who opts out on your site does not automatically opt out inside your app. The choice transfers only when that person logs in to both with the same account. That lets your CMP recognize them and apply the earlier decision. Ask your CMP provider how it handles this, because the answer decides whether your customers set their preferences once or twice.
How to Implement the GPP on Your Website
There are 2 ways to implement GPP on your site, depending on whether you employ developers or use a CMP. Your first option is building the signal yourself from the specifications the IAB Tech Lab publishes, and your second is subscribing to a consent management platform that does the work for you.
The GPP GitHub route suits publishers with in-house engineering. Your business will need to budget for maintenance once implemented. Updates land twice a year, and each new state law adds a section your code has to produce.
Most sites take the second route of using a CMP that handles GPP integration for you. Before you sign, check:
- State coverage
- GPC detection
- Delivery of the string into your ad stack
A CMP that displays a banner correctly counts for nothing when the signal never reaches your ad server.
Work through the following GPP checklist in order:
- List the states and countries your visitors come from.
- Check that your CMP covers every one of them.
- Switch the GPP on, and set the location rules.
- Send state strings unless you have signed the MSPA.
- Turn on GPC detection so a browser opt-out counts as an opt-out.
- Test a live page and confirm the signal reaches your advertising partners.
- Update your Privacy Policy to match what you now disclose.
Step 6 is the one businesses often forget, yet it is the most important. It determines whether any of the earlier work counts and whether you are compliant or not.
How Users Enable the GPP (via the GPC)
Users do not install the GPP; they enable a compatible opt-out signal instead. The GPP reads a choice someone already made in their browser, so the signal has to come from the GPC.
Browsers handle the GPC in different ways. The Brave and DuckDuckGo browsers send it by default, Firefox offers it as a setting, and users of other browsers add it through an extension such as Privacy Badger from the Electronic Frontier Foundation (EFF), Disconnect, or OptMeowt. The Global Privacy Control site publishes the current list along with instructions for each option.
The GPC site reports more than 150 million users and over 66,000 participating websites, as seen below. This means that a portion of your traffic already arrives with the opt-out switched on.

A site running the GPP honors that choice as the page loads, without asking the person to click a banner. A site without it keeps processing data for people who already said no, exposing the business to compliance risks.
When to Use the GPP (and When You Don't Need It)
GPP is not for every site. Here's how to tell whether your business needs it. Use GPP if you need to do one or more of the following:
- Comply with US state privacy laws such as the CCPA, the Connecticut Data Privacy Act (CTDPA), and the Virginia Consumer Data Protection Act (VCDPA).
- Work with vendors, ad exchanges, or header bidding partners (buyers who compete for your ad space in real time) that expect a GPP signal.
- Serve ads or collect data across several jurisdictions (the EU, the US, Canada).
- Manage several regional privacy strings and want one framework to hold them.
- Automate opt-out signalling so a browser setting reaches your partners without manual work.
You do not need the GPP when no partner asks for it. A site that runs no advertising, or that works with vendors handling consent their own way, gets by with simpler regional consent. In practice, that means a banner that applies one set of rules per region. Ask your advertising partners before you decide, since they set the requirement.
The GPP Timeline (2021-Today)
GPP didn't appear overnight, with the specification taking 18 months to reach a finished form. It has changed every year since, as shown in the table below.
| Date | Action |
| March 9, 2021 | The IAB Tech Lab released the GPP for public comment as 1 of 4 Project Rearc standards |
| June 1, 2022 | The IAB Tech Lab unveiled the GPP and opened a 60-day public comment period |
| September 28, 2022 | The consent string specification reached final form |
| June 2023 | GPP 1.1 arrived, and the Consent Management API remains on that version today |
| January 31, 2024 | The legacy US Privacy String reached deprecation |
| February 2025 | The IAB Tech Lab renamed the standard to Global Privacy Protocol and finalized the implementation guidelines |
| October 2025 | Sections arrived for Maryland, Indiana, Kentucky, and Rhode Island, alongside a commitment to twice-yearly releases from 2026 |
| Today | 20 US state sections sit alongside the European TCF, the Canadian TCF, and the MSPA US National string |
Every year has added jurisdictions. Therefore, it makes sense to build the predictable, six-monthly release cycle of the IAB Tech Lab into a twice-yearly review.
GPP String Anatomy: Sections, Headers, and Section IDs (Technical Deep-Dive)
A GPP string holds the privacy preferences of one visitor for every jurisdiction that applies to them, packed into a single encoded value. The GPP string anatomy has 2 parts: a header and one or more sections, joined by a tilde character.
| Part | Role |
| Header | Acts as a table of contents, listing the sections in the string and the order they come in. |
| Sections | Carry the disclosures and choices, with one block per framework or law |
The GPP header structure works as a table of contents but contains no consent choices, making it small and quick to parse. A vendor reads it first, learns that a California section and a European section sit inside, and jumps straight to the one that concerns it.
The following screenshot is a real example from the IAB Tech Lab specification, followed by a breakdown of each part and its function.

Below, we have broken it down into distinct pieces:
| Piece | What it is |
| DBACNY | The header, declaring 2 sections and their order |
| CPXxRfAPXxRfAAfKABENB-CgAAAAAAAAAAYgAAAAAAAA | The EU TCF section |
| 1YNN | The legacy US Privacy section |
| ~ | The separator between each part |
Every framework gets a numeric GPP section ID, and those IDs are what the header lists.
| Section ID | Framework |
| 2 | EU TCF |
| 5 | Canadian TCF |
| 6 | US Privacy (deprecated) |
| 7 | MSPA US National |
| 8 to 27 | The 20 individual US state sections |
IDs 3 and 4 belong to the header itself and to a signal integrity feature, which is why the jurisdiction numbering skips them.
What sits inside a section depends on the law behind it. A European section mirrors the TC String, recording which purposes the visitor agreed to, which vendors received disclosure, the legal basis claimed for each purpose, and a timestamp marking when the consent happened. A US state section carries that state opt-out flags instead, covering sale, sharing, targeted advertising, and sensitive data, plus a separate block recording whether the browser sent a GPC signal.
Your CMP assembles all of this, working out which laws apply to the visitor, building a section for each one, listing those section IDs in the header, and joining everything into the string your ad requests carry.
The older signals live here too. The US Privacy string and the TC String became sections 6 and 2 respectively, so neither travels on its own anymore. To check that the configurations on your site are correct, paste a string into the decoder the IAB Tech Lab publishes, and check that the header lists a section for every state your visitors come from. A missing section means a missing signal.
GPP Implementation Checklist (Step-by-Step)
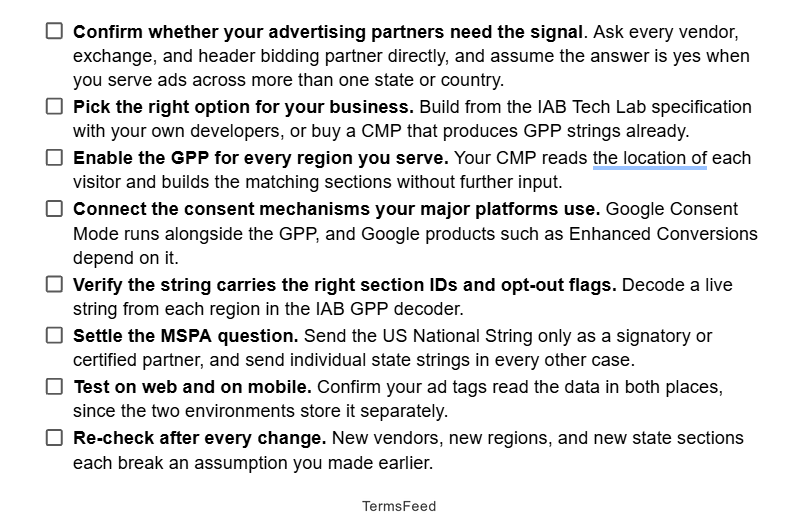
GPP implementation takes 8 steps, and each one ends with a test that proves it worked. Download, print, and check off this checklist, which covers how to implement GPP from the first vendor conversation through to the ongoing review. Keep a dated copy as a record that you are checking the GPP signal is doing its job.
☐ Confirm whether your advertising partners need the signal. Ask every vendor, exchange, and header bidding partner directly, and assume the answer is yes when you serve ads across more than one state or country.
☐ Pick the right option for your business. Build from the IAB Tech Lab specification with your own developers, or buy a CMP that produces GPP strings already.
☐ Enable the GPP for every region you serve. Your CMP reads the location of each visitor and builds the matching sections without further input.
☐ Connect the consent mechanisms your major platforms use. Google Consent Mode runs alongside the GPP, and Google products such as Enhanced Conversions depend on it.
☐ Verify the string carries the right section IDs and opt-out flags. Decode a live string from each region in the IAB GPP decoder.
☐ Settle the MSPA question. Send the US National String only as a signatory or certified partner, and send individual state strings in every other case.
☐ Test on web and on mobile. Confirm your ad tags read the data in both places, since the two environments store it separately.
☐ Re-check after every change. New vendors, new regions, and new state sections each break an assumption you made earlier.
Download the GPP Implementation Checklist as a PDF file.
Download the GPP Implementation Checklist.

Verifying the string and testing on web and mobile are the steps businesses commonly miss. However, they are the only 2 that prove the earlier work reached anybody.
GPP and Google Consent Mode / Ad-Platform Requirements
If you run Google Ads or Analytics, GPP plugs into your consent signaling. Google reads 2 separate signals: Consent Mode for the tags on your pages and the GPP string for your ad requests. Your CMP produces both from the single choice a visitor makes.
The table below shows the key differences between Google Consent Mode and the GPP.
| Google Consent Mode | GPP | |
| What it governs | The Google tags on your pages, covering Ads and Analytics | Ad requests to Ad Manager, AdSense, and AdMob, plus every non-Google partner |
| What it carries | Whether the visitor allows cookie storage, use of advertising data, and ad personalization | The privacy choices of the visitor, encoded per jurisdiction |
| What an opt-out triggers | Cookieless pings instead of stored identifiers | Restricted data processing at Google, and equivalent limits elsewhere |
Neither mechanism replaces the other, and if your site runs Google advertising, it needs both. Major ad platforms, including Google, support GPP/US privacy strings, resulting in consistent global signaling.
Google Consent Mode governs the tags themselves. Tags do not write or read advertising cookies when a user denies consent, sending pings without cookies instead. A GPP-aware CMP will auto-enable the right Google Consent Mode integrations so tags behave in accordance with the consent choices of the user.
However, the role of the GPP is different. Google Ad Manager reads the string from the gpp and gpp_sid parameters on each ad request. An opt-out triggers restricted data processing, so ads keep serving without the personalization the visitor declined.
There are important limitations to consider with Ad Manager. As shown below, Ad Manager accepts 6 sections, covering US National, California, Colorado, Connecticut, Florida, and Virginia, and it declines the IAB Canada TCF, the US Privacy String, Utah, and the IAB Europe TCF inside a GPP string.

Website owners have 2 routes to close the gap. Firstly, send the US National string once you sign the MSPA, since Google accepts that section and it speaks for every state at once. Secondly, switch restricted data processing on directly for the states Google leaves out, using the rdp=1 setting in your Google ad tags, which works without any GPP section behind it.
Working with a GPP-aware CMP means standardized signals lower what an opt-out costs you. Ads keep serving under restricted data processing, so you lose the personalization yet keep the inventory. Consent Mode estimates the conversions you no longer attribute, so your reporting stays usable. Consent flips both signals the other way, and your tracking, attribution, and remarketing run in full. Every platform reading the string applies the same logic, and Prebid, a widely used header bidding software, passes it to each buyer unchanged.
It's crucial to configure Consent Mode alongside the GPP so the consent state reaches your Google tags. Your CMP holds one decision and writes it to 2 places: the Consent Mode parameters for the tags and the GPP string for the ad requests. Test both on a live page, because a CMP configured for one and not the other looks correct in the dashboard while the signal never reaches your advertising partners.
GPP Glossary: Key Terms Cheatsheet
Our GPP glossary covers 18 terms in one place to assist you in navigating your obligations.
| Term | Definition |
| CMP | A Consent Management Platform, the software that collects consent on your site and builds the GPP string |
| Consent Mode | The Google mechanism that tells Google tags whether a visitor allows cookies, advertising data use, and ad personalization |
| DNT | Do Not Track, the earlier browser signal, which failed because no law required a site to honor it |
| DSAR | A data subject access request, meaning a request from a person to see, correct, or delete the personal data you hold |
| GPC | The Global Privacy Control, the leading UOOM, which sends a "do not sell or share my personal information" flag |
| GPP | The IAB Tech Lab protocol that carries the privacy choices of a visitor across the advertising supply chain, renamed Global Privacy Protocol in February 2025 |
| GPP header | The opening part of a GPP string, listing which sections sit inside it and in what order |
| GPP section and Section ID | A numbered block inside a GPP string, holding the disclosures and choices for one framework or law |
| GPP string | The single encoded value carrying the privacy choices of one visitor for every jurisdiction that applies to them |
| IAB Tech Lab | The technical standards arm of the Interactive Advertising Bureau, which develops and maintains the GPP |
| MSPA | The IAB Multi-State Privacy Agreement, a standard contract setting out how signatories interpret US state privacy laws |
| National Approach | The defined term in the MSPA under which signatories apply one standard that meets the strictest state requirement |
| Project Rearc | The IAB Tech Lab initiative launched in February 2020 to rebuild digital advertising around consumer privacy, which produced the GPP |
| TC String | The encoded record of what a visitor agreed to under the TCF, which now travels as a GPP section |
| TCF | The IAB Europe Transparency and Consent Framework, which handles consent under the GDPR, with version 2.3 mandatory from March 1, 2026 |
| UOOM | A universal opt-out mechanism, meaning a browser or device setting that sends an opt-out to every site a person visits |
| US National String | The GPP section that answers every US state law at once, reserved for MSPA signatories and certified partners |
| USPrivacy string | The legacy CCPA signal, deprecated on January 31, 2024, and now carried as GPP section 6 |
Keep this table next to the implementation checklist. It helps clear up any misunderstandings when different parties use terms differently.
GPP and Ad Performance: Does Honoring Opt-Outs Hurt Campaigns?
A common worry: does supporting GPP cost you ad performance? Supporting the GPP does not necessarily reduce overall advertising performance, although reduced personalization may affect some advertising use cases.
Firstly, the reach you lose is because of the law. A visitor who opts out leaves your addressable audience whether or not you run the GPP. The only thing you control is whether you learn about it in a machine-readable form or hear about it from a regulator.
Secondly, ads keep serving to people who opt out. An opt-out recorded in the string triggers restricted data processing at Google and equivalent limits elsewhere. You keep the impression and lose only the personalization behind it.
Thirdly, everyone who consents stays fully addressable. The same string confirms that permission to every vendor at once, so tracking, remarketing, and conversion measurement run in full for the majority of your traffic.
Where losses show up is when signalling is inconsistent. Vendors handling the same visitor differently produce double suppression, dropped bids, and attribution numbers that never reconcile. One standardized string removes that variance, which is why GPP conversions reporting holds together better with the standard in place than without it.
Using GPP lets you optimize your ad performance while complying with global laws. Remember that structured data from people who agreed beats unreliable data about everyone. The GPP keeps the first group clearly separated from the second.
IAB GPP: Frequently Asked Questions
The following 10 frequently asked questions cover what businesses most often want to know about the IAB Global Privacy Platform, from the legal position through to implementation.
The IAB Global Privacy Platform (GPP) is a technical protocol from the IAB Tech Lab. It carries the privacy choices of a visitor across the digital advertising supply chain. It packs those choices into one encoded GPP string covering every jurisdiction that applies to that person. The IAB Tech Lab renamed it the Global Privacy Protocol in February 2025, and the acronym stayed the same.
No law requires businesses to use the GPP, because no privacy law names the GPP or any other specific technology or protocol. The laws require you to honor opt-out signals, and the GPP has become the standard mechanism for carrying those signals to your advertising partners. There are 12 states that now impose that duty, and the legacy US Privacy String reached deprecation in January 2024, which leaves no IAB-maintained alternative.
No, the GPP is not a universal opt-out mechanism (UOOM). A UOOM is a browser or device setting a person switches on, which then sends an opt-out to every site they visit. The GPP reads that setting and carries the resulting choice to your vendors, so the two work as a pair.
The GPC is a signal a user sends, and the GPP is the protocol that transports it. The Global Privacy Control flags "do not sell or share my personal information" on every site a person visits. The GPP records that flag in the relevant state section and passes it down the supply chain. The CCPA and CPRA require businesses to honor a GPC signal.
The GPP covers many jurisdictions at once while the TCF handles consent for European law alone. The TCF became a section inside the GPP, so a European implementation keeps working unchanged.
A CMP collects consent, and the GPP transmits it. A Consent Management Platform shows the banner, records what each visitor chose, and stores the result. The GPP is the format that carries those choices to the ad tech vendors who act on them. A CMP with GPP support does both jobs together.
The GPP supports 4 families of privacy strings: the IAB Europe TCF string, the IAB Canada TCF string, the MSPA US National string, and individual strings for 20 US states. The IAB Tech Lab adds sections as new state laws take effect.
Only MSPA signatories and MSPA-certified partners can use the US National String. Sending it without signing asserts that you follow the National Approach of the MSPA, which the IAB warns amounts to a material misrepresentation. Everyone else sends individual state strings.
Implement the GPP either by building the signal from the IAB Tech Lab specification or by using a CMP that produces GPP strings already. Most sites take the second route. If you do, confirm that your CMP covers every state your visitors come from, detects the GPC, and passes the string through to your ad server.
Users do not enable the GPP, but they switch on a compatible opt-out signal instead. Brave and the DuckDuckGo browser send the Global Privacy Control by default, Firefox offers it as a setting, and other browsers support it through an extension. Your site reads that signal and records it in the GPP string.
Do You Need a GPP-Ready Privacy Policy?
GPP signals your consent choices, but your Privacy Policy explains what you do with the data. Therefore, every business working in GPP-covered jurisdictions needs a GPP-ready Privacy Policy. Here are 3 reasons why:
- Disclosures: A GPP string records that a visitor received notice and chose their preferences, and your Privacy Policy is where that notice lives.
- Legal duty: State privacy laws impose the disclosure duty directly. A GPP signal tells your vendors what a visitor chose, but your Privacy Policy is responsible for telling the user what information you collect.
- Regulatory requirement: Regulators will compare your Privacy Policy and GPP signals. An enforcement review looks at what you disclose alongside what your signals claim, and any gaps create potential regulatory breaches.
A GPP Privacy Policy covers 4 things. It names the data you collect, the purposes and vendors behind that collection, the opt-out rights available to each visitor, and the ways to exercise them, including universal opt-out mechanisms such as the GPC.
The California CCPA/CPRA require businesses that sell or share personal information to post a "Do Not Sell or Share My Personal Information" link. In some circumstances, businesses rely on opt-out preference signals instead of maintaining a separate "Do Not Sell or Share My Personal Information" link, subject to the requirements of the CPPA regulations. The regulations call this processing signals in a frictionless manner. Businesses must state this in their Privacy Policy, as shown below in a screenshot from the CCPA.

Before worrying about GPP signals, make sure your Privacy Policy is fit for purpose. The TermsFeed Privacy Policy Generator builds a policy covering the collection, the vendors, and the opt-out rights your GPP implementation refers back to. The TermsFeed Cookie Consent solution handles the banner alongside it.
Summary and Key Takeaways
The IAB Global Privacy Platform gives you one signal that answers many of the jurisdictions your visitors come from. Here are the 8 key takeaways every website owner needs to know.
- The IAB Global Privacy Platform is a protocol from the IAB Tech Lab, which carries privacy and consent choices across the advertising supply chain as a single standardized string.
- The GPP is not legally mandatory, and 12 US states require you to honor the opt-out signals it carries.
- The GPP supports the IAB Europe TCF, the IAB Canada TCF, the MSPA US National string, and individual sections for 20 US states, with updates arriving twice a year.
- The GPP reads the Global Privacy Control and records it, without being a universal opt-out mechanism itself.
- The GPP works alongside a CMP, which collects the consent that the GPP then standardizes and transmits.
- The US National String belongs to MSPA signatories and certified partners alone, and everyone else sends individual state strings.
- Implementation runs either through the IAB Tech Lab specification on GitHub or through a CMP that produces GPP strings already, while your visitors switch on a UOOM such as the GPC at their end.
- Your Privacy Policy says what you collect, and a GPP signal says only what a visitor chose. California lets you drop the Do Not Sell link only if you process opt-out preference signals in a frictionless manner and say so in your Privacy Policy.
Before your business considers GPP signals, your Privacy Policy must be right. It's the first thing a regulator reads, and the most accurate GPP signal counts for nothing if your policy is missing, vague, or out of date.

The first step to compliance: A Privacy Policy.
Stay compliant with our agreements, policies, and consent banners — everything you need, all in one place.